Coding Tools
CodeQL 2.27.2 updates analysis and breaks macOS 27 support
GitHub Changeloghigh confidence
Why it matters
- →New C++ regex and Comdb2 SQL-injection models improve detection of specific vulnerability classes.
- →macOS 27 support is broken due to Apple's removal of multi-architecture binaries, requiring toolchain downgrades.
- →Refined Rust async data flow and C# false positive fixes increase scanning precision for enterprise users.
GitHub has released CodeQL 2.27.2, an incremental update to its static analysis engine that enhances security query coverage for C++, Go, Rust, and JavaScript. Key improvements include ECMAScript regex parsing in C++, new SQL-injection sinks for Comdb2, and refined data flow tracking for Rust async blocks. The release also addresses false positives in C# XSS and clickjacking detection. Crucially, the update removes support for macOS 27 and Xcode 27 because Apple discontinued the required multi-architecture binaries, breaking traced analysis for compiled languages on those versions. GitHub automatically deploys this version to github.com users, while Enterprise Server users must wait for a future release or upgrade manually.
Read originalThe story around this
Earlier coverage that leads up to this article, and what followed. Lines connect each piece to the closest one after it, converging here.
How we got here
- 1Claude Code v2.1.219 Update Released
Claude Code Releases · July 25, 2026 · Background
- 2llama.cpp b10172 Release Fixes and Enhancements
llama.cpp Releases · July 29, 2026 · Background
- 3CodeQL 2.26.1 Enhances Analysis Accuracy
GitHub Changelog · July 29, 2026 · Same story
- 4Claude Code v2.1.225 Update Released
Claude Code Releases · August 10, 2026 · Background
- 5CodeQL 2.27.0 adds support for Linux ARM64
GitHub Changelog · September 9, 2026 · Same story
- 6llama.cpp b11020 adds DeepSeek V3.2/V4 parser support
llama.cpp Releases · September 18, 2026 · Background
More from GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
Copilot adds sandboxing and Claude Haiku 5.5
GitHub Copilot is tightening the leash on autonomous agents with local sandboxing, a critical step for enterprise security that restricts file, network, and credential access. The update also brings Claude Haiku 5.5 to all paid tiers, expanding the model lineup available within the IDE. Meanwhile, the CLI now integrates seamlessly with local Ollama instances, allowing developers to swap between cloud and local models without leaving their workflow. These changes shift Copilot from a simple autocomplete tool toward a more controlled, multi-model agent platform.
GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
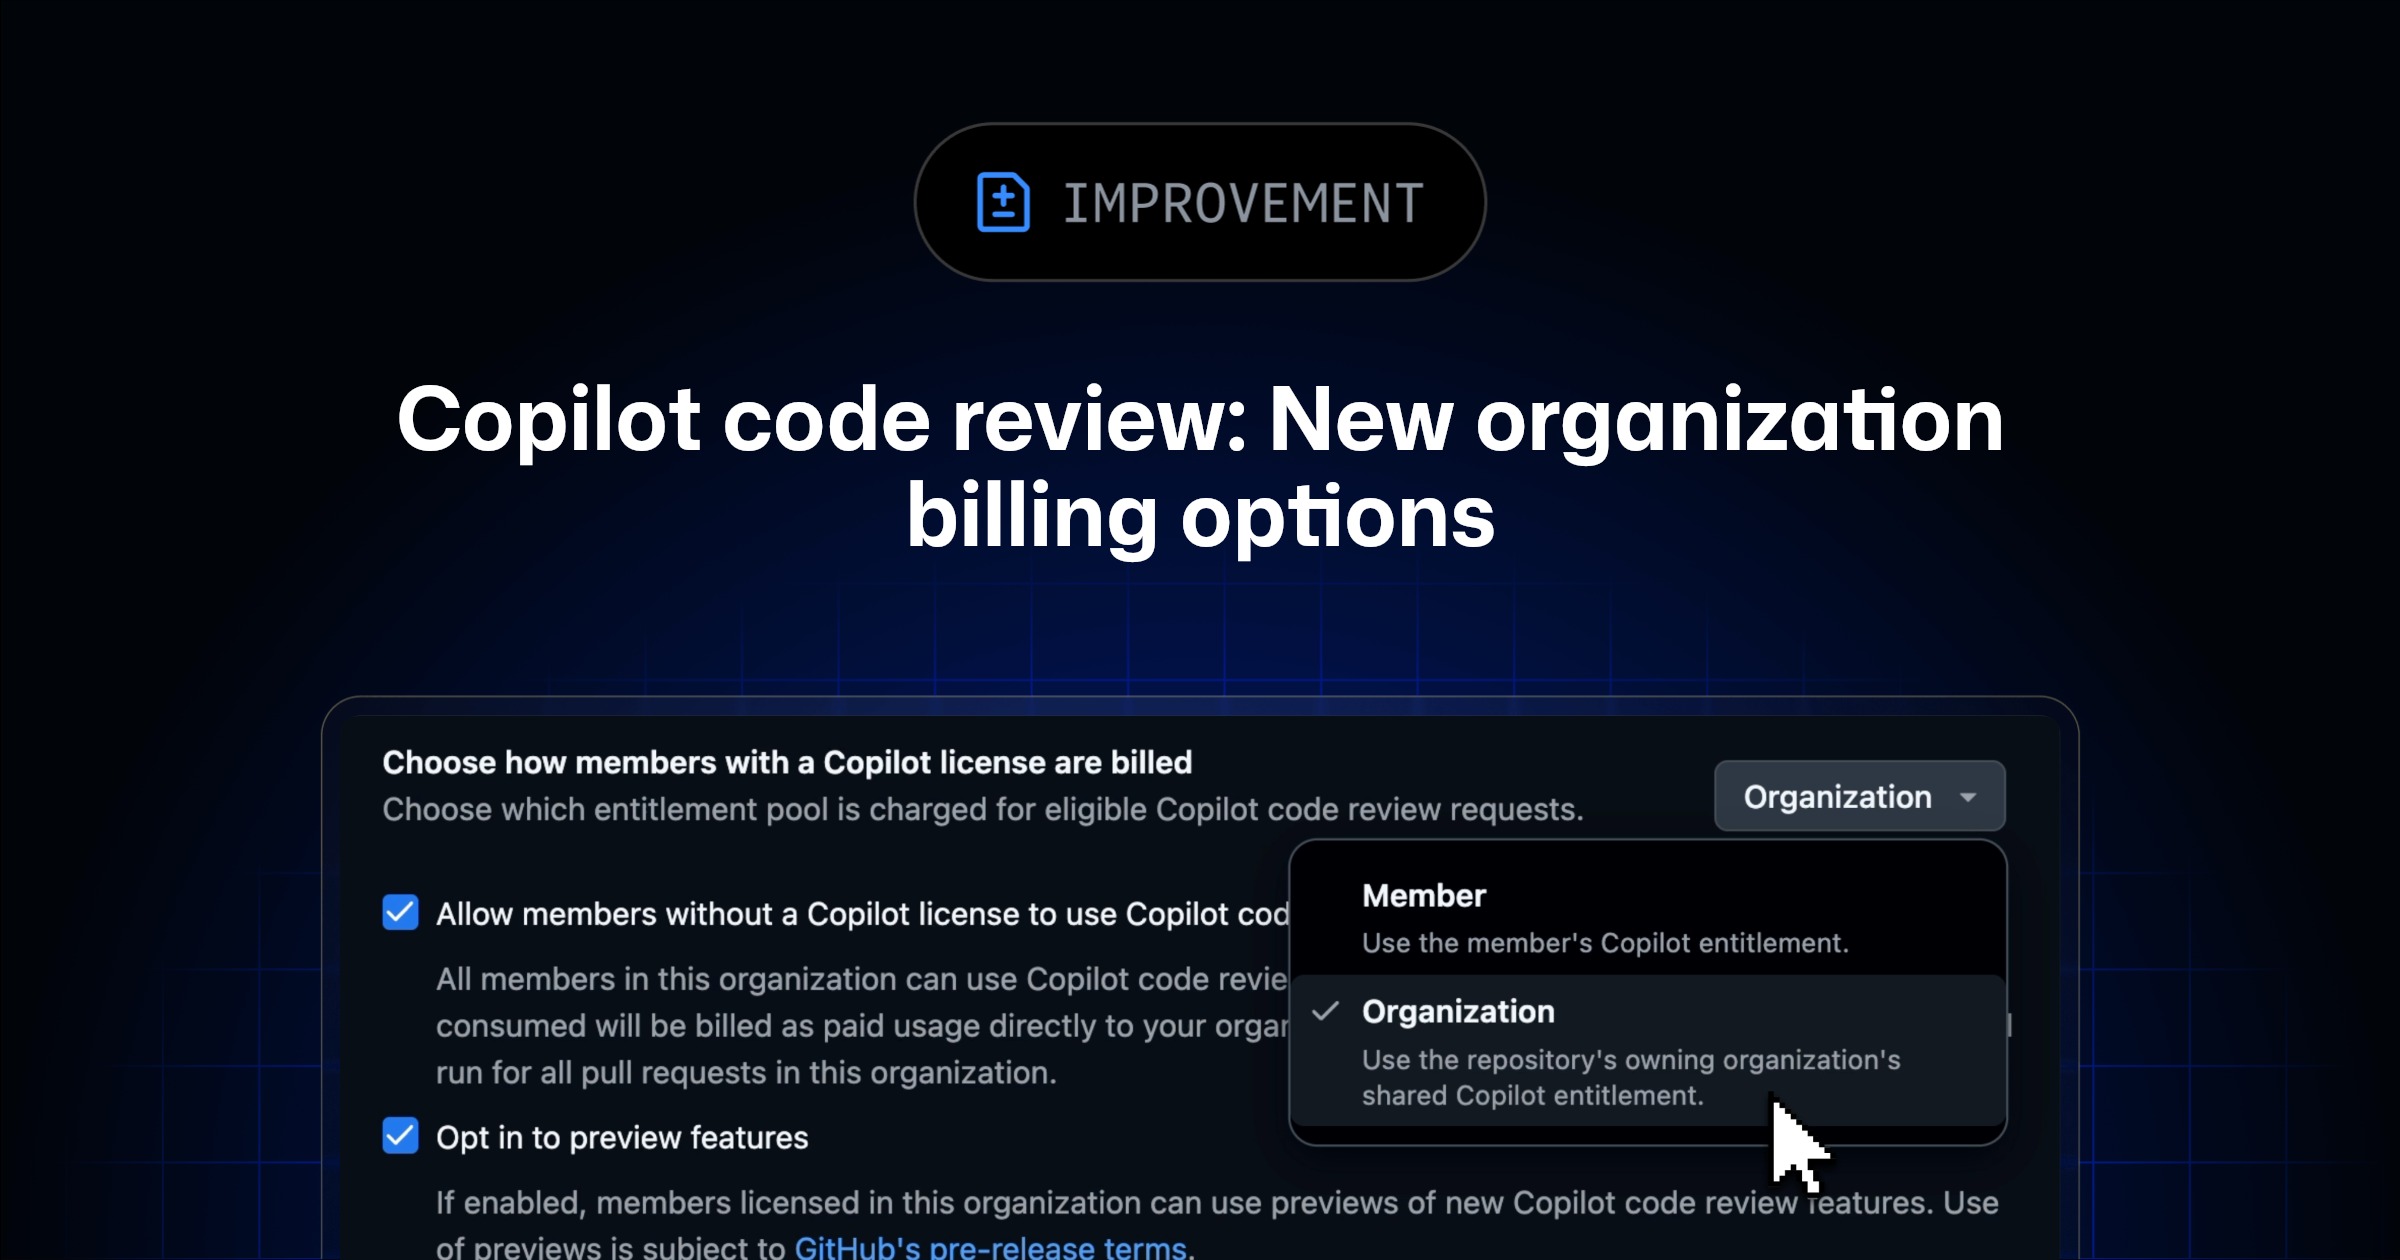
GitHub Copilot Code Review adds org billing controls
GitHub is tightening the leash on enterprise AI spending with new billing and access controls for Copilot Code Review. Organizations can now shift costs from individual member quotas to a central cost center using AI Credits, preventing personal license exhaustion from halting team workflows. Simultaneously, admins can block external licenses from triggering reviews, ensuring only authorized corporate accounts consume resources. This moves Copilot from a perk to a managed utility, giving finance teams actual visibility into AI consumption.
GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
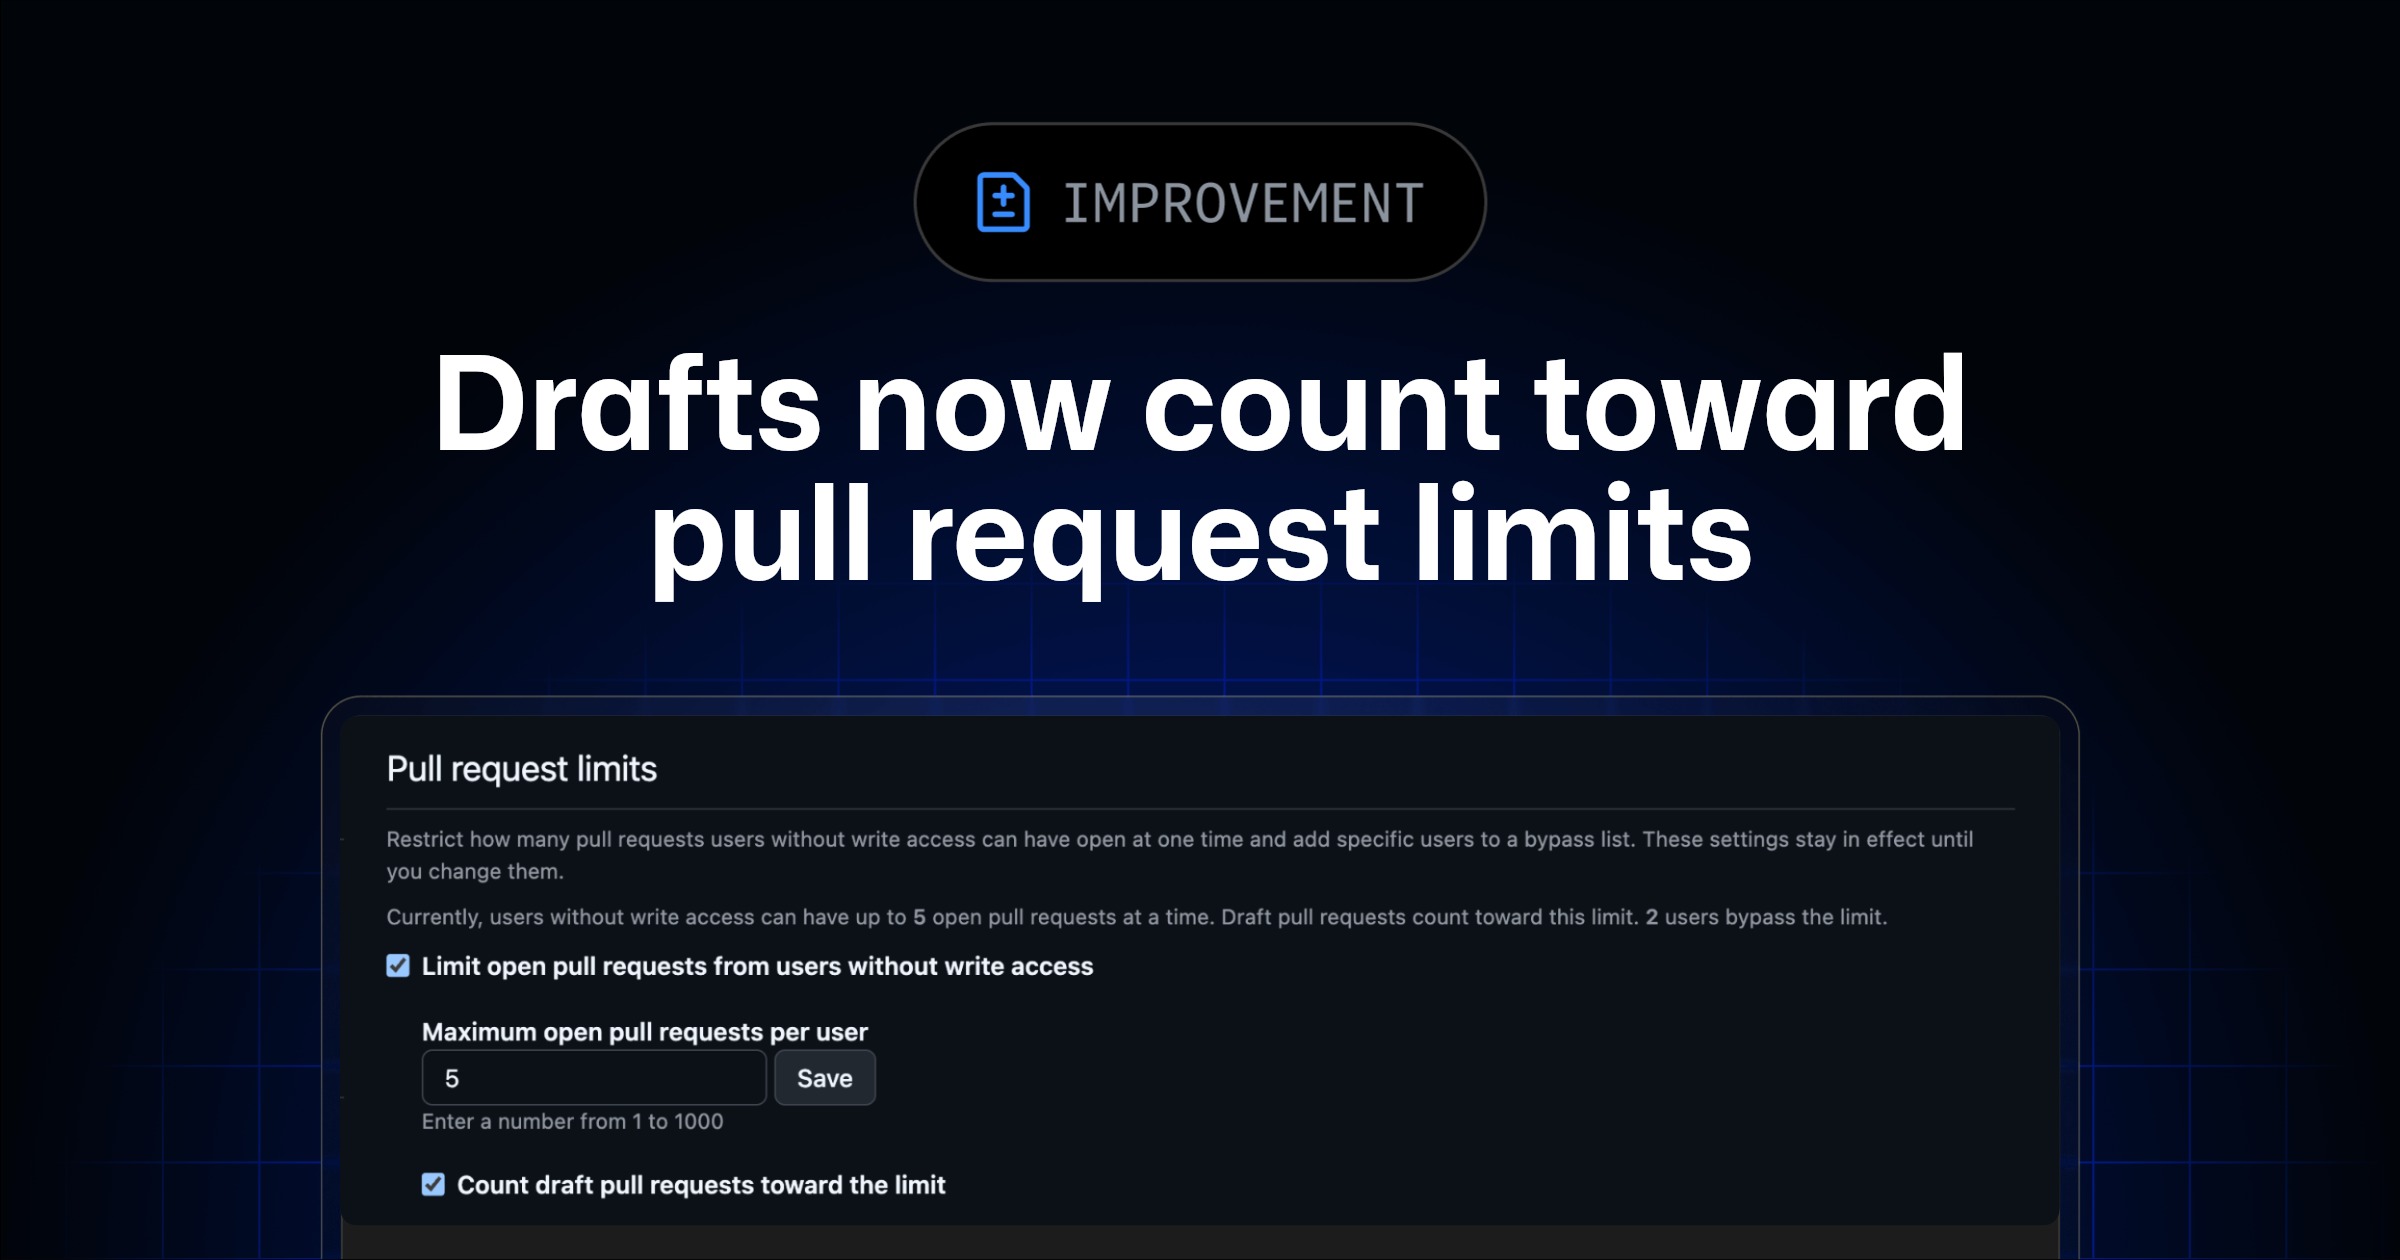
GitHub draft PRs now count toward limits
GitHub finally plugs a loophole that let spammers bypass repository pull request limits by opening endless drafts. Maintainers can now configure these limits to include draft PRs, directly reducing notification clutter and wasted CI runs from low-quality contributions. This is a practical quality-of-life fix for open source maintainers tired of managing spam rather than code. It shifts the burden slightly toward contributors but protects repository health.
GitHub Changelog
More in Coding Tools
Coding Toolscoding
Claude Code v2.1.292 patches security and agent logic
This release tightens the leash on Claude Code's autonomous capabilities while fixing critical sandbox escapes. The new effort parameter for Agent tools lets developers explicitly control sub-agent depth, a necessary guardrail as these systems grow more complex. Security fixes are prominent, addressing how plugins handle network paths and how file permissions persist during session resumption. It’s a stability patch that ensures the tool remains usable in enterprise environments without compromising on the new agent features.
Claude Code Releases
Coding Toolscoding
Claude Code v2.1.293 updates Haiku and fixes agent bugs
Anthropic quietly shipped a significant model update alongside routine maintenance. Claude Haiku 5.5 is now the default on the API, offering a 1M context window at $0.10 per million tokens, which lowers the cost floor for high-volume coding tasks. The release also patches critical stability issues in the local agent runtime, specifically fixing memory leaks in HTTP MCP connections and resolving session state corruption during context compaction. These fixes matter because they stabilize the autonomous coding workflow that developers rely on daily. With Haiku 5.5 now standard, teams can deploy cheaper, faster iterations without manual configuration.
Claude Code Releases
Coding Toolscoding
Claude Code v2.1.294 fixes hook logic
Anthropic quietly patched a frustrating edge case in Claude Code’s agent hooks. Previously, instructions like 'Block commands that...' were often ignored because the model didn't recognize them as valid blocking criteria. This update ensures those prompts are properly interpreted, while also refining how stop conditions are judged to prevent premature termination. It’s a small but necessary fix for anyone relying on strict guardrails in automated coding workflows.
Claude Code Releases