Market & Regulation
UK Launches Rapid AI Delivery Taskforce for Military
Siftedhigh confidence
Why it matters
- →The RAID taskforce aims to modernize military operations with AI, potentially transforming decision-making processes.
- →Slow procurement processes could hinder the growth of startups and delay AI integration in defence.
- →Aligning intent with execution is crucial for the taskforce to achieve its goals and support domestic SMEs.
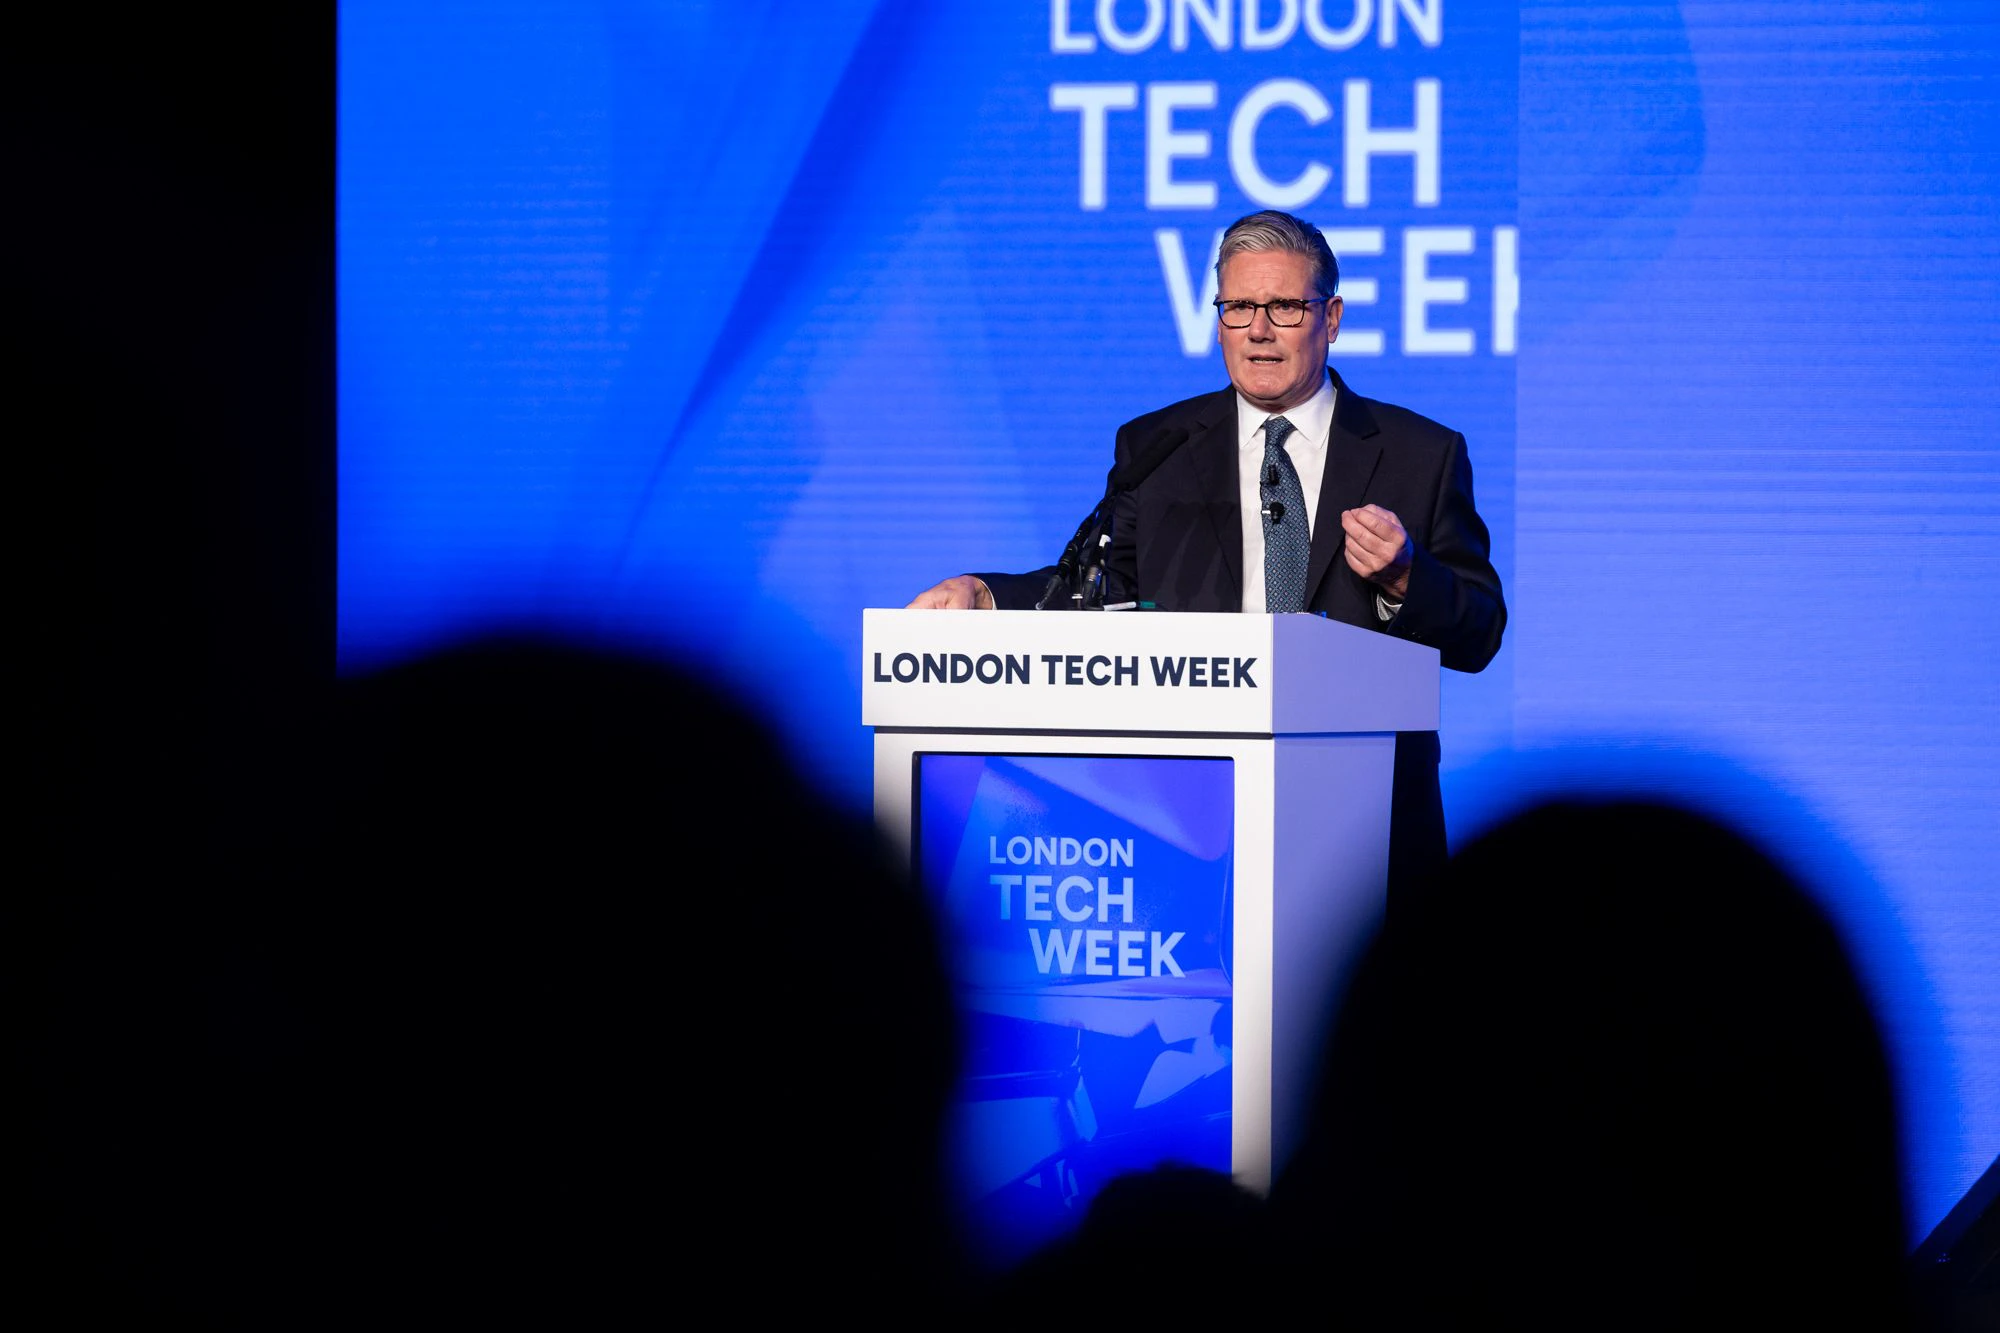
The UK has launched the Rapid AI Delivery (RAID) taskforce to speed up the integration of AI in its military operations. Announced during London Tech Week, the initiative aims to improve decision-making and reduce risks for military personnel. However, concerns have been raised about the Ministry of Defence's slow procurement processes, which could impede the taskforce's effectiveness. Despite the potential benefits, the success of RAID will depend on overcoming these bureaucratic challenges to truly transform defence technology adoption.
Read originalThe story around this
Earlier coverage that leads up to this article, and what followed. Lines connect each piece to the closest one after it, converging here.
More from Sifted
More in Market & Regulation
 © TechCrunch AI
Market & Regulationbusiness
Crusoe cancels $1.25B Boom turbine deal
The collapse of Crusoe’s $1.25 billion order for Boom Supersonic’s stationary turbines exposes the fragility of AI infrastructure financing. While Crusoe raised $3.9 billion, it pivoted away from on-site gas generation, opting instead for grid power and diverse energy mixes. This signals that even well-funded data center operators are prioritizing flexibility over massive, long-term capital commitments to specialized hardware. Boom’s pivot to sell jet engines as power plants was a bold bet on AI energy needs, but losing its anchor customer suggests the market is more cautious than anticipated.
TechCrunch AI
 © TechCrunch AI