Market & Regulation
GitHub Introduces MCP Allowlists for Enterprises
GitHub Changeloghigh confidence
Why it matters
- →Provides enterprises with enhanced security control over AI tool usage.
- →Allows customization of server access to ensure compliance with organizational policies.
- →Empowers teams to manage their own settings within a secure framework.
GitHub has introduced a new feature for enterprise users to control access to Model Context Protocol (MCP) servers through allowlists. This feature allows enterprise owners to specify which MCP servers GitHub Copilot clients can use, enhancing security by blocking untrusted servers. The allowlists can be configured in the enterprise managed settings, and teams can override these settings to tailor them to their needs. This update is available for the GitHub Copilot app, Copilot CLI, and VS Code, providing enterprises with greater control over their AI tool usage.
Read originalThe story around this
Earlier coverage that leads up to this article, and what followed. Lines connect each piece to the closest one after it, converging here.
How we got here
- 1GitHub EMU IP Allow List Now Generally Available
GitHub Changelog · June 8, 2026 · Same story
- 2
More from GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
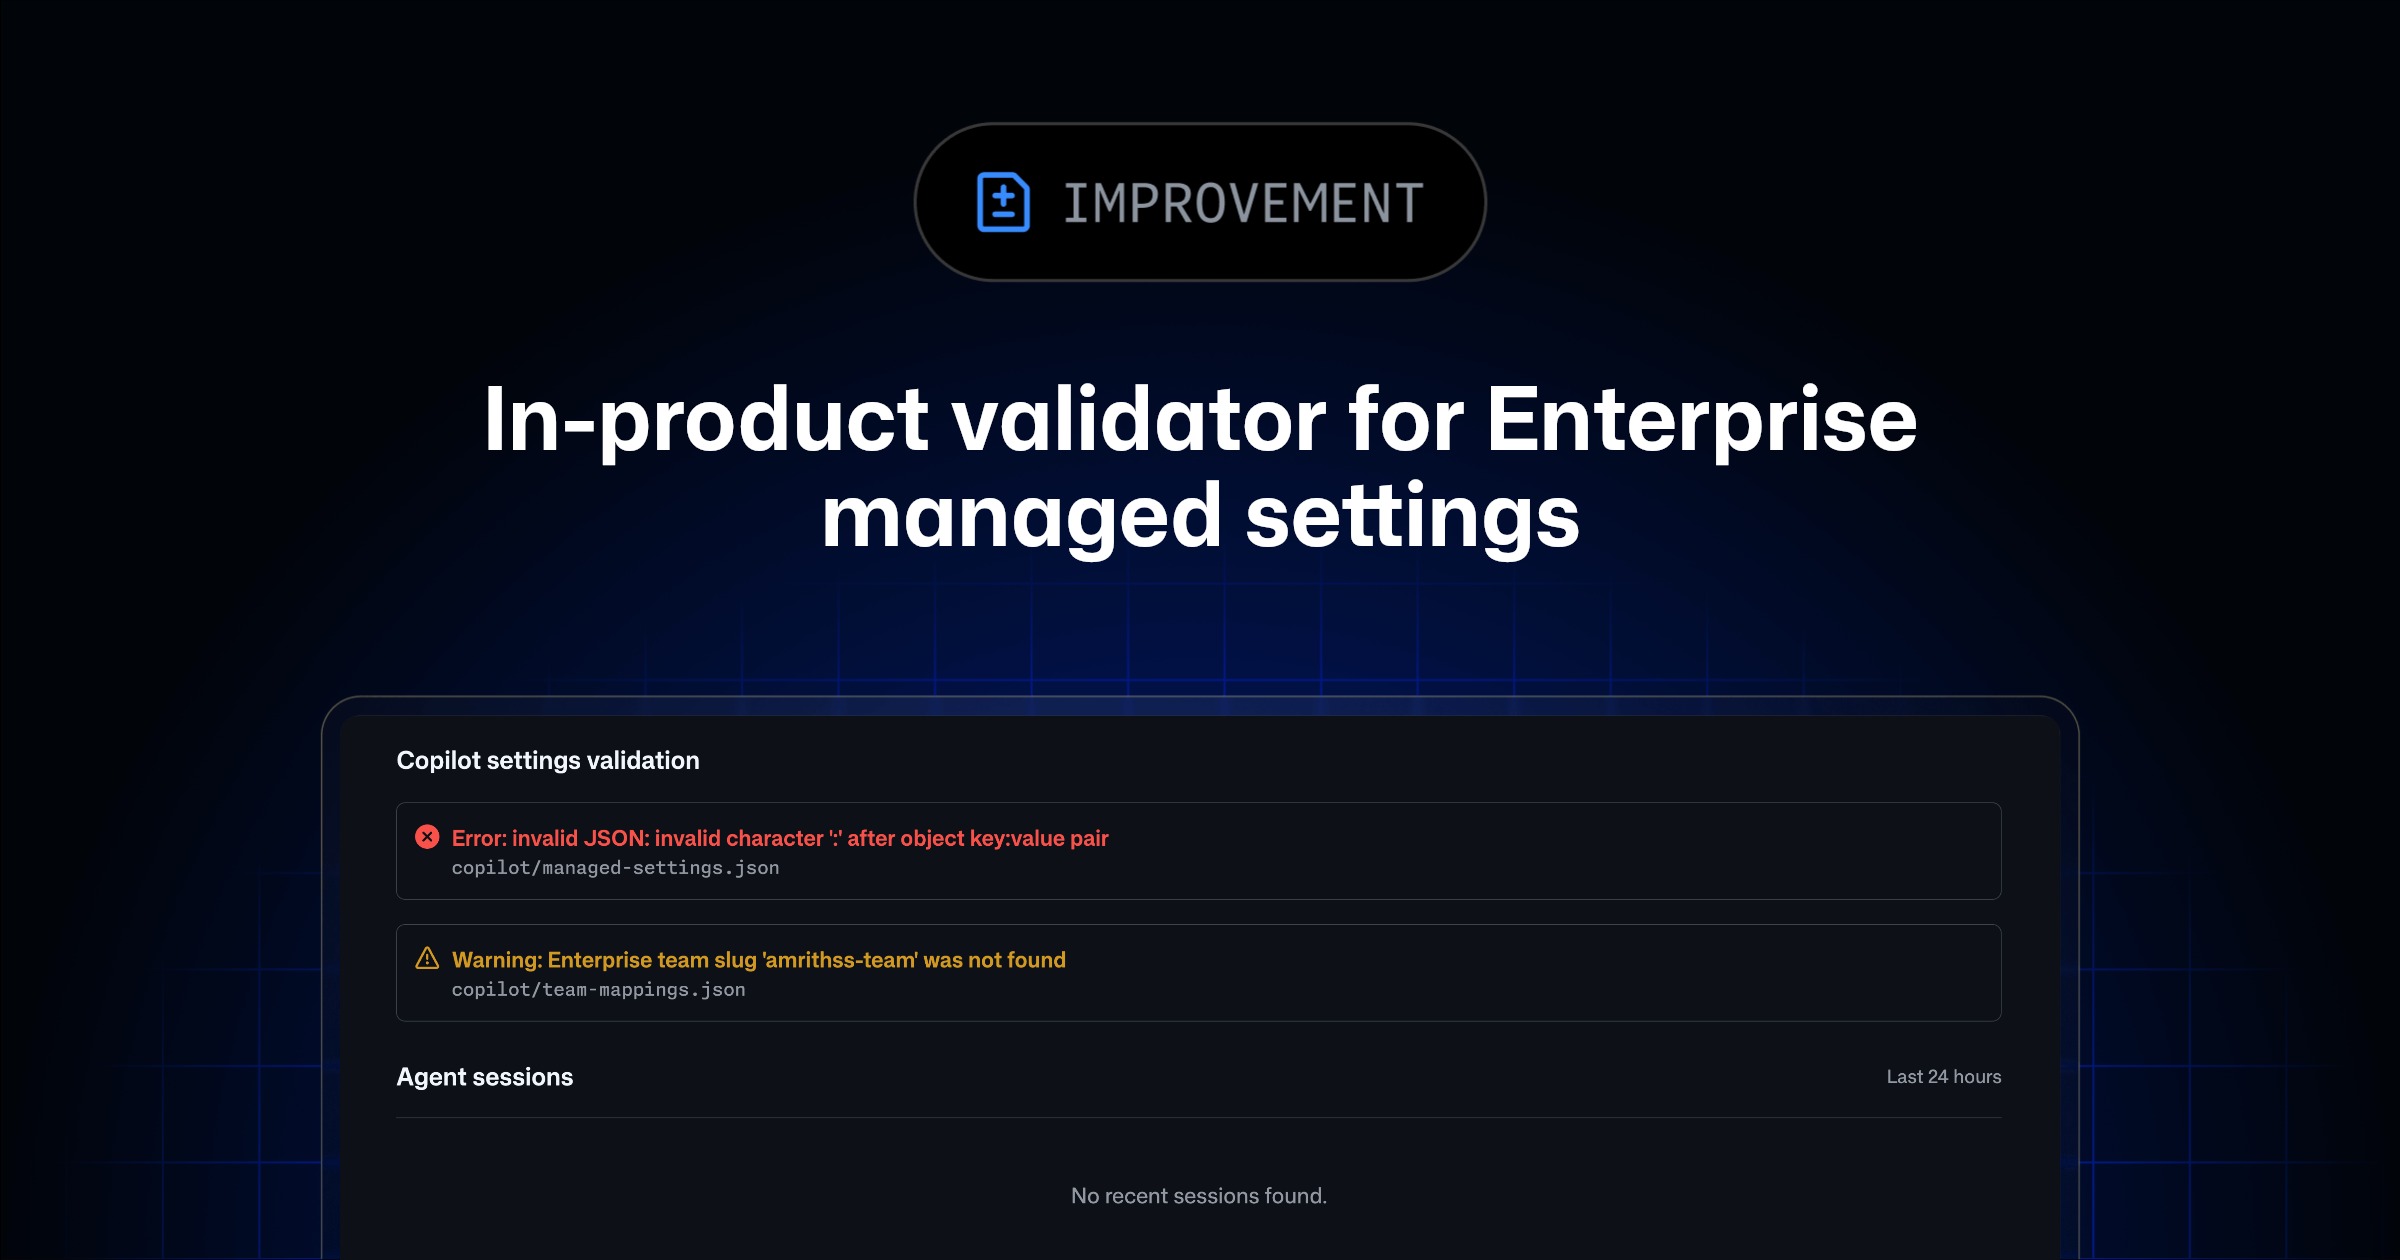
GitHub Copilot adds in-product settings validator
GitHub Copilot now validates enterprise managed settings directly in the UI, catching malformed JSON and invalid team mappings before they break policy enforcement. This shifts validation from a silent failure mode to an explicit feedback loop, saving admins from debugging why their AI controls aren't applying. By pointing to specific files and JSON paths, it reduces the friction of managing .github-private repositories at scale. It’s a pragmatic fix for a common enterprise pain point rather than a new capability.
GitHub Changelog
 © GitHub Changelog
More in Market & Regulation
 © TechCrunch AI
Market & Regulationbusiness
Crusoe cancels $1.25B Boom turbine deal
The collapse of Crusoe’s $1.25 billion order for Boom Supersonic’s stationary turbines exposes the fragility of AI infrastructure financing. While Crusoe raised $3.9 billion, it pivoted away from on-site gas generation, opting instead for grid power and diverse energy mixes. This signals that even well-funded data center operators are prioritizing flexibility over massive, long-term capital commitments to specialized hardware. Boom’s pivot to sell jet engines as power plants was a bold bet on AI energy needs, but losing its anchor customer suggests the market is more cautious than anticipated.
TechCrunch AI
 © TechCrunch AI