Coding Tools
GitHub Secret Scanning adds Lovable and Supabase detectors
GitHub Changeloghigh confidence
Why it matters
- →Developers using Supabase or Lovable now have automated protection against accidental credential exposure.
- →GitHub deepens its integration with modern AI and database infrastructure providers.
- →Reduces the window of vulnerability for compromised keys in public repositories.
GitHub has updated its secret scanning service to automatically detect credentials from Lovable Labs, Pydantic Services, and Supabase. Under the secret scanning partnership program, detected secrets in public repositories are forwarded to the respective providers for immediate revocation or rotation. This integration enhances security posture for developers using these platforms by automating the identification of exposed keys. The update applies to new secret types added to GitHub's detection database.
Read originalThe story around this
Earlier coverage that leads up to this article, and what followed. Lines connect each piece to the closest one after it, converging here.
How we got here
- 1GitHub CI Migrates to Hugging Face Jobs
Hugging Face Blog · June 9, 2026 · Background
- 2GitHub Expands Secret Scanning Capabilities
GitHub Changelog · June 17, 2026 · Same story
- 3GitHub Expands Secret Scanning Coverage
GitHub Changelog · August 7, 2026 · Same story
More from GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
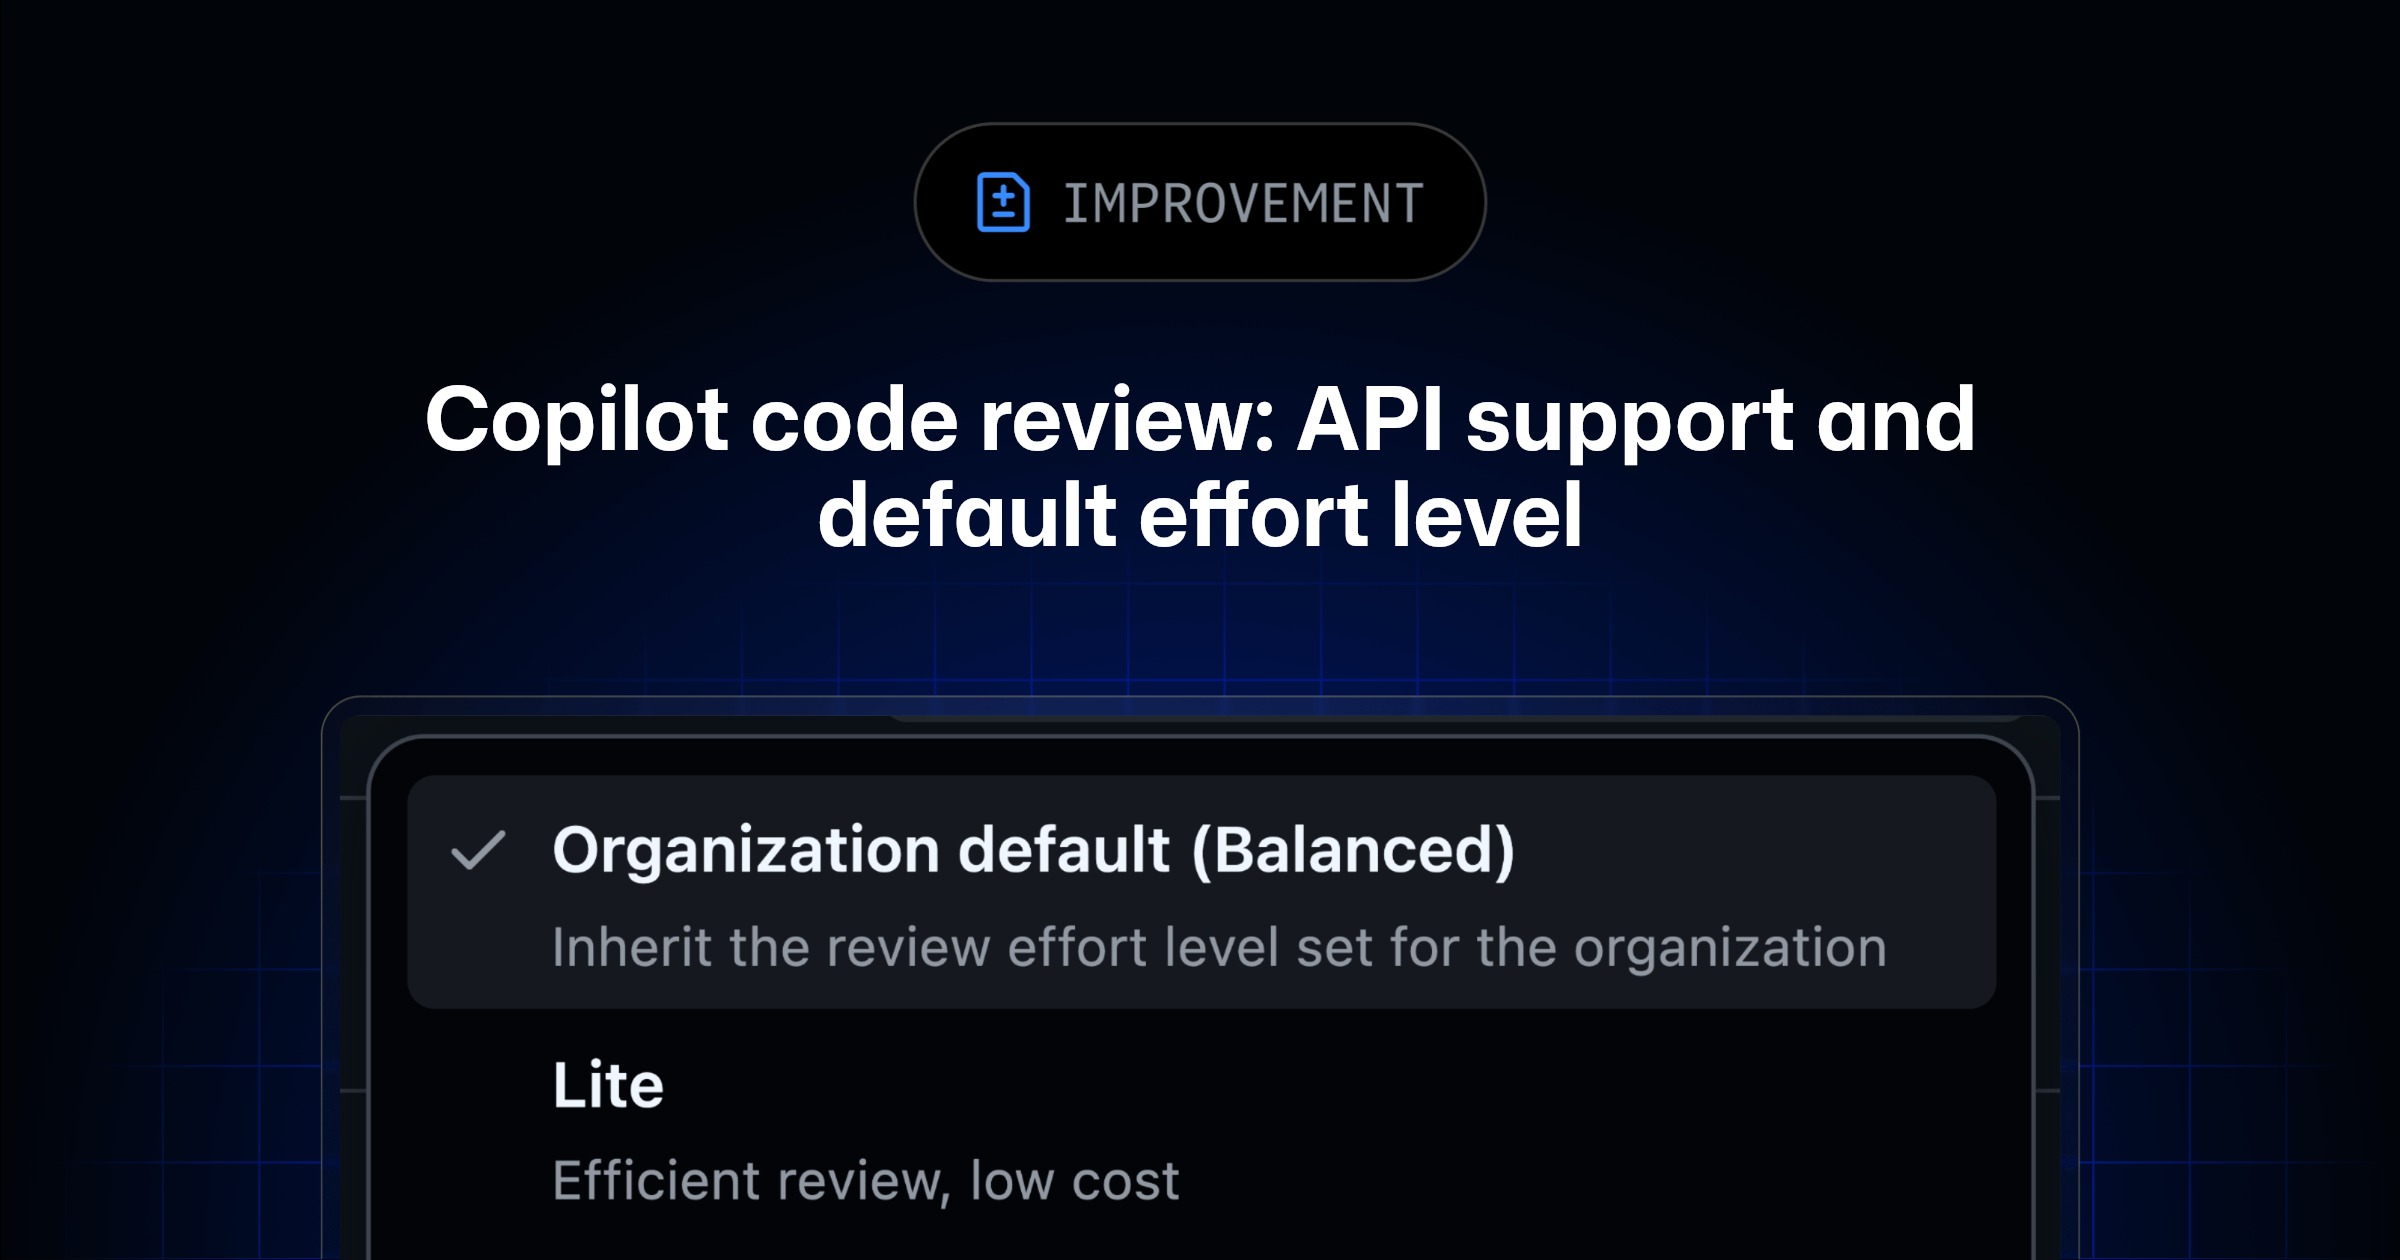
GitHub Copilot Code Review API and Default Effort Change
GitHub finally exposes Copilot code review to external automation via REST and GraphQL APIs, moving it from a manual UI action to an integrable pipeline step. This allows developers to trigger reviews directly from scripts or internal tools rather than relying on the web interface. Simultaneously, the default effort level shifts to Balanced, striking a middle ground between speed and depth for most repositories. While Lite remains available for those prioritizing raw throughput, the API access is the real win here, enabling true CI/CD integration for automated code quality checks.
GitHub Changelog
 © GitHub Changelog
Market & Regulationother
npm trusted publishing configs expire in 48 hours
npm is tightening security on its trusted publishing feature by imposing a strict 48-hour expiration window for unvalidated configurations. This change directly targets supply chain risks where repository ownership changes could hijack trust relationships before they are fully vetted. Once a configuration successfully publishes, it becomes permanent, but any shift in project identity forces a fresh validation cycle. Additionally, tokens from GitHub Actions issue_comment events are now blocked, pushing developers toward safer triggers like push or release. This is a necessary hardening of the npm ecosystem that prioritizes security over convenience.
GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
npm staged publishing now supports new package creation
npm has closed a major gap in its staged publishing workflow by allowing the creation of entirely new packages directly from the staging queue. Previously, developers had to perform an initial public publish before they could leverage the safety net of staged releases for subsequent versions. This update enables automated workflows to initialize scoped and unscoped packages securely using granular access tokens, ensuring that the very first version also undergoes maintainer review before becoming installable. It effectively removes the manual friction from setting up secure, review-gated package lifecycles.
GitHub Changelog
More in Coding Tools
Coding Toolscoding
Claude Code v2.1.290: Plugin hooks and agent stability fixes
This release significantly tightens the security model for Claude Code plugins by exposing server tool IDs and approval ceilings to hook functions, allowing developers to build more granular permission checks. It also stabilizes long-running agent sessions by fixing critical bugs in subagent resume logic and scheduled task persistence after compaction. For plugin authors, the new validation flags ensure gating hooks are properly configured before deployment. These changes make the platform safer for enterprise use while reducing friction for complex automated workflows.
Claude Code Releases
Coding Toolscoding
llama.cpp b11424 adds CUDA 13 and ROCm 10.0
This release quietly closes the hardware gap for local inference by adding default support for CUDA 13 and ROCm 10.0 alongside existing CUDA 12 builds. NVIDIA users can now leverage newer driver stacks without manual configuration, while AMD GPU owners finally get first-class parity with the same ease of use previously reserved for CUDA. Apple Silicon KleidiAI is disabled in this specific build, a notable regression for Mac users who rely on that optimization. The inclusion of Snapdragon and OpenVINO binaries further broadens the reach to edge devices and Intel hardware. It’s less about new features and more about llama.cpp solidifying its position as the universal runtime for every major accelerator.
llama.cpp Releases
Coding Toolscoding
llama.cpp b11425 adds ROCm 10 and Snapdragon support
This release quietly cements llama.cpp as the universal inference runtime by finally bringing first-class ROCm 10.0 support to both Linux and Windows. AMD GPU users no longer need workarounds, effectively closing a long-standing parity gap with NVIDIA's CUDA ecosystem. The inclusion of Snapdragon AI stack binaries for Linux marks a strategic push into ARM-based edge devices, while the simultaneous addition of CUDA 13 builds ensures compatibility with the latest driver stacks. By standardizing these hardware backends across major operating systems, the project removes friction for developers deploying models on diverse non-NVIDIA hardware.
llama.cpp Releases