Coding Tools
GitHub Copilot adds Claude Opus 5.5 and GPT-6
GitHub Changeloghigh confidence
Why it matters
- →Access to Claude Opus 5.5 and GPT-6 Sol provides developers with top-tier reasoning models directly within their IDE.
- →Local sandboxing and OpenTelemetry support address key enterprise security and observability requirements for AI agents.
- →Assisted approvals and session rewinding improve the safety and usability of autonomous coding workflows.
GitHub has released weekly updates to its Copilot suite, introducing Claude Opus 5.5 and GPT-6 Sol for Pro+ and Enterprise plans, alongside GPT-6 Luna and Grok 4.7 for broader tiers. The update emphasizes agent security and observability with new local sandboxing capabilities that limit file and network access, plus OpenTelemetry integration for tracking agent activity. Additional features include assisted approvals for low-risk tool calls, the ability to rewind agent sessions by editing earlier messages, and improved Dev Container support for remote hosts. These changes position Copilot as a more robust, enterprise-ready platform for autonomous coding tasks.
Read originalMore from GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
GitHub Copilot adds in-product settings validator
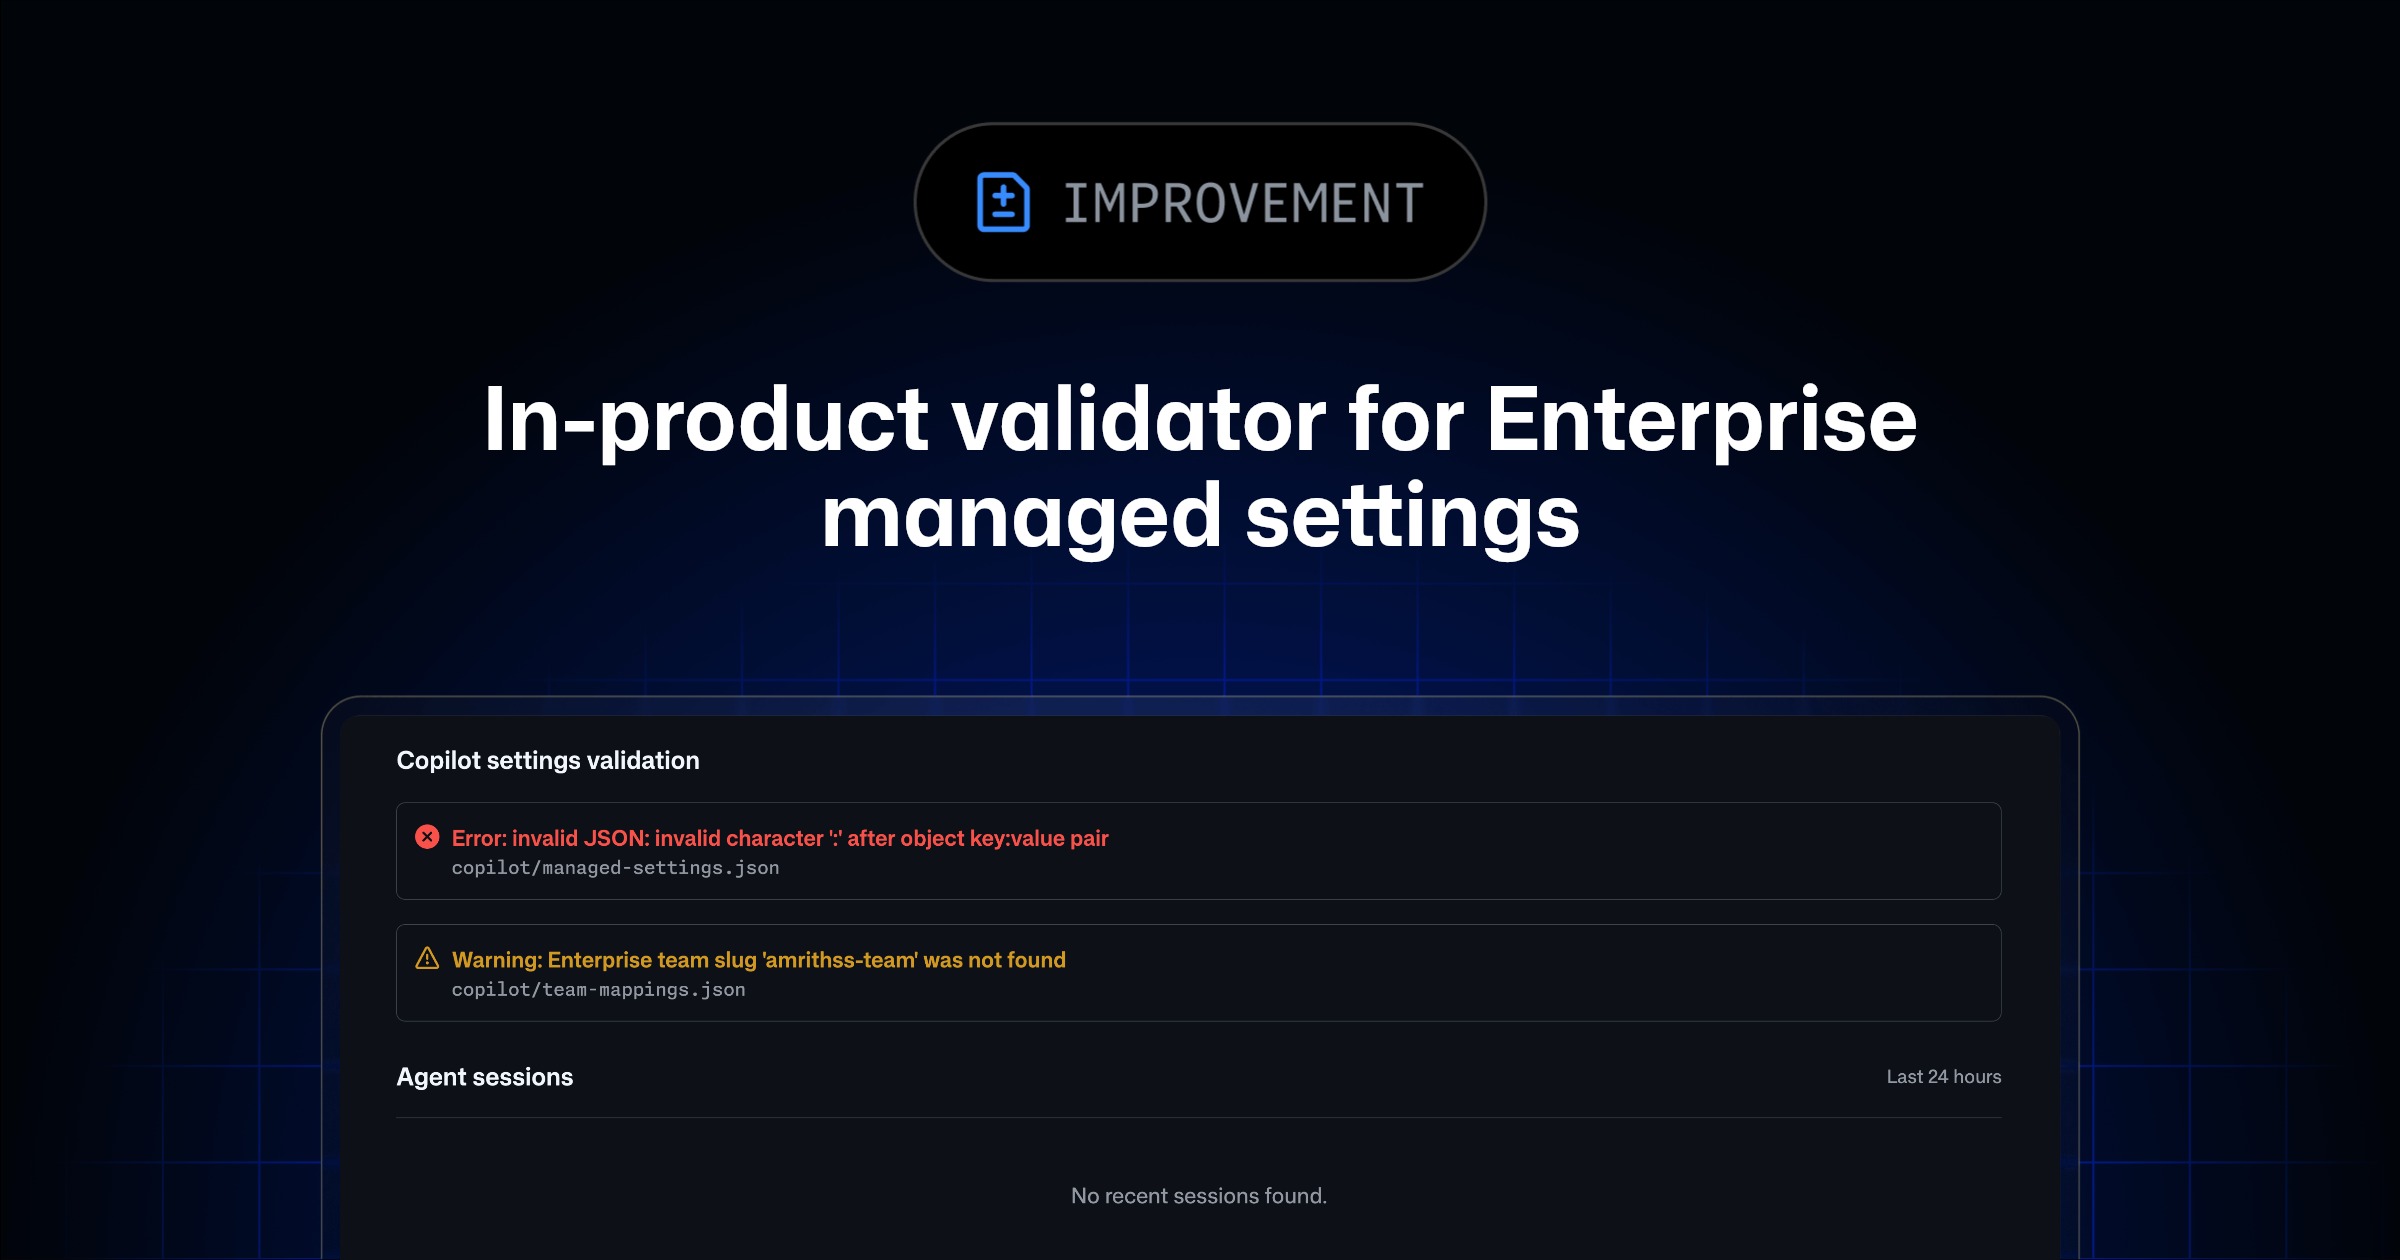
GitHub Copilot now validates enterprise managed settings directly in the UI, catching malformed JSON and invalid team mappings before they break policy enforcement. This shifts validation from a silent failure mode to an explicit feedback loop, saving admins from debugging why their AI controls aren't applying. By pointing to specific files and JSON paths, it reduces the friction of managing .github-private repositories at scale. It’s a pragmatic fix for a common enterprise pain point rather than a new capability.
GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
GitHub Copilot metrics now track PR review stages
GitHub finally exposes the hidden latency in pull request workflows through its Copilot usage metrics API. By breaking down merge times into median and p90 durations for ready-to-first-review, first-to-final review, and final-to-merge stages, teams can pinpoint exactly where bottlenecks occur. This granular visibility distinguishes between waiting for initial attention versus lingering in approval queues, allowing for targeted process fixes rather than guessing. Since it ignores bot reviews, the data reflects genuine human collaboration speed, offering a clear signal on team efficiency.
GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
Copilot Agentic Autofix Now Uses Memory
GitHub is connecting its agentic autofix to Copilot Memory, turning isolated bug fixes into institutional knowledge. Instead of patching a security alert once and forgetting it, the agent now records the resolution pattern for future use. This allows the system to preemptively handle similar vulnerabilities across the repository and share secure coding habits with other tools like code review agents. It shifts Copilot from a reactive fixer to a proactive teacher that learns your team's specific security posture over time.
GitHub Changelog
More in Coding Tools
Coding Toolscoding
Claude Code v2.1.282 patches critical session and UX bugs
This release stabilizes Claude Code by fixing a cascade of session-breaking errors that previously caused silent data loss or API drops. The most significant fix addresses resumed conversations re-sending messages in altered forms, which was corrupting reasoning traces and breaking extended thinking workflows. It also resolves persistent login refresh loops and managed setting parsing failures that plagued enterprise deployments. While the changelog is dense with UI tweaks like scrollbar fixes and vim mode corrections, the core value lies in restoring reliability for long-running agent sessions.
Claude Code Releases
Coding Toolscoding
Claude Code v2.1.283: Gateway hints and plugin fixes
This release quietly solves a major pain point for enterprise AI workflows by adding gateway hint headers, allowing LLM gateways to correctly group requests per user prompt instead of treating them as isolated events. The new managed settings for availableModelsMatch and deniedModels give organizations precise control over model access, blocking specific versions even when broader allowances exist. Beyond governance, the update stabilizes the plugin ecosystem with rigorous validation checks that prevent silent failures from broken or misconfigured extensions. These changes shift Claude Code from a developer tool to a manageable enterprise component.
Claude Code Releases
Coding Toolscoding
llama.cpp b11183 splits Metal FA kernels
This release quietly refactors how llama.cpp handles Flash Attention on Apple Silicon by splitting kernels into per-dtype libraries. It’s a structural optimization that likely reduces memory overhead and improves compilation times for Metal users, though the immediate performance gains are subtle compared to algorithmic leaps. The build matrix remains massive, adding ROCm 10.0 and CUDA 13.4 support while disabling KleidiAI on Apple Silicon for now. This is infrastructure maintenance rather than a feature breakthrough, but it keeps the runtime robust across the expanding landscape of hardware backends.
llama.cpp Releases