Market & Regulation
GitHub Adds AI Credit Pool Management in Billing UI
GitHub Changeloghigh confidence
Why it matters
- →Simplifies AI credit management by integrating it into the billing UI.
- →Automatically adjusts credit limits based on licenses, reducing manual oversight.
- →Provides better financial control by allowing users to manage overages and usage limits.
GitHub has introduced a new feature in its billing UI that allows users to manage AI credit pools for cost centers directly, a task that previously required the GitHub REST API. This update is available for Copilot Business and Enterprise users on GitHub Enterprise Cloud. The system automatically calculates the credit pool limit based on the number of licenses, and users can choose to block usage or allow overages when limits are reached. This feature helps ensure that cost centers do not exceed their allocated AI credits, providing better financial control.
Read originalThe story around this
Earlier coverage that leads up to this article, and what followed. Lines connect each piece to the closest one after it, converging here.
How we got here
- 1GitHub Copilot shifts to token-based billing
AI News · June 2, 2026 · Related
- 2
More from GitHub Changelog
 © GitHub Changelog
Coding Toolscoding
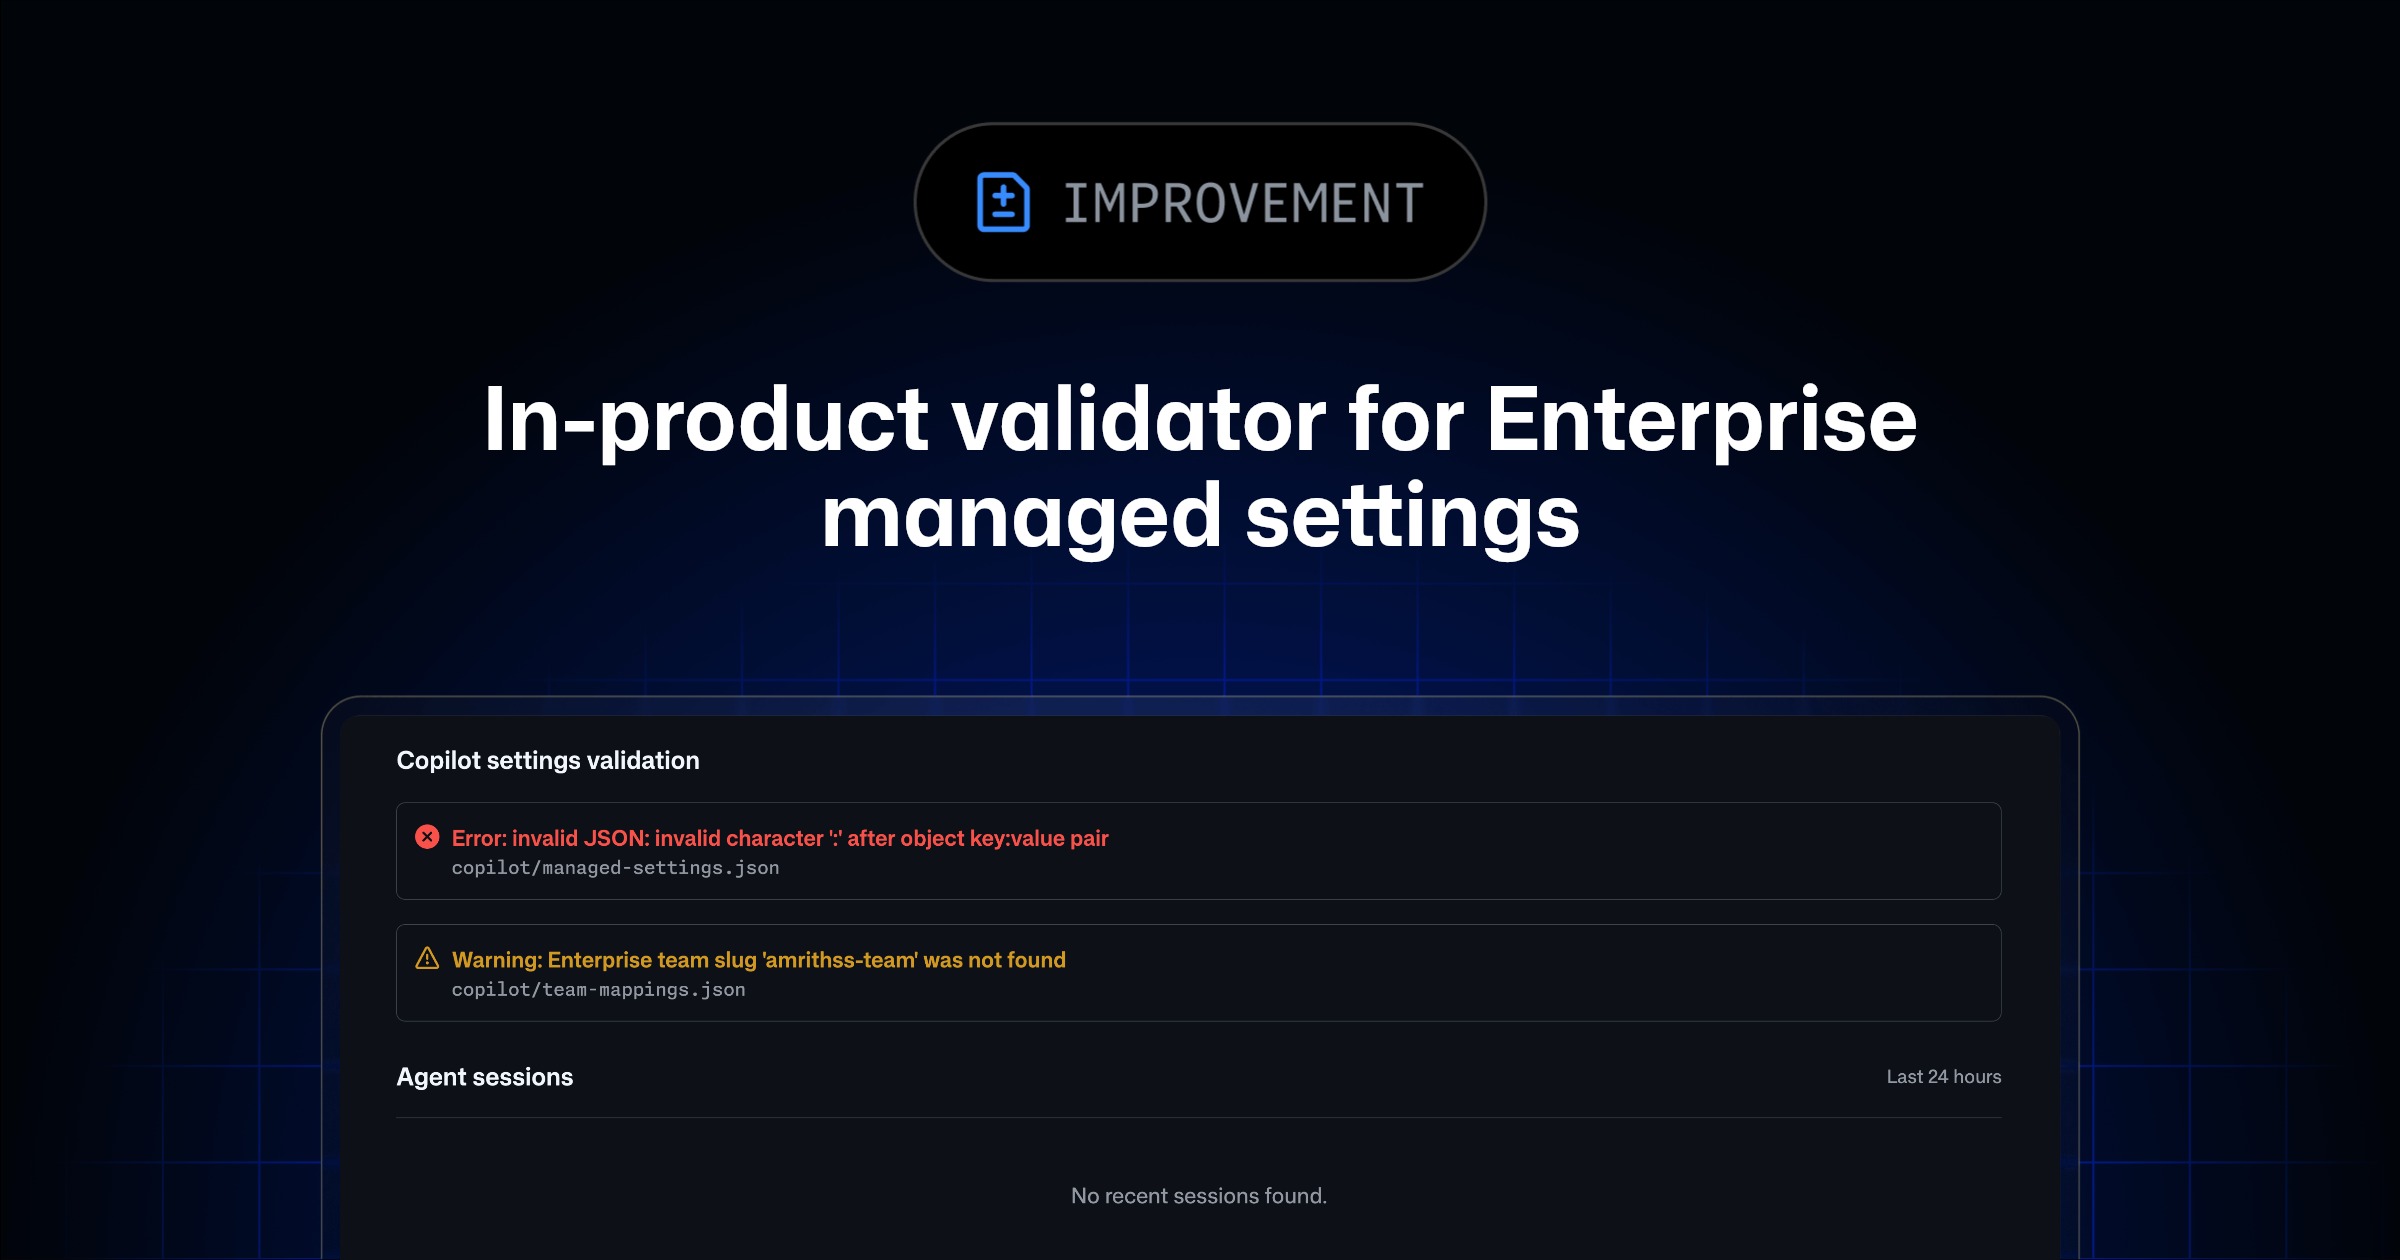
GitHub Copilot adds in-product settings validator
GitHub Copilot now validates enterprise managed settings directly in the UI, catching malformed JSON and invalid team mappings before they break policy enforcement. This shifts validation from a silent failure mode to an explicit feedback loop, saving admins from debugging why their AI controls aren't applying. By pointing to specific files and JSON paths, it reduces the friction of managing .github-private repositories at scale. It’s a pragmatic fix for a common enterprise pain point rather than a new capability.
GitHub Changelog
 © GitHub Changelog
More in Market & Regulation
 © TechCrunch AI
Market & Regulationbusiness
Crusoe cancels $1.25B Boom turbine deal
The collapse of Crusoe’s $1.25 billion order for Boom Supersonic’s stationary turbines exposes the fragility of AI infrastructure financing. While Crusoe raised $3.9 billion, it pivoted away from on-site gas generation, opting instead for grid power and diverse energy mixes. This signals that even well-funded data center operators are prioritizing flexibility over massive, long-term capital commitments to specialized hardware. Boom’s pivot to sell jet engines as power plants was a bold bet on AI energy needs, but losing its anchor customer suggests the market is more cautious than anticipated.
TechCrunch AI
 © TechCrunch AI